News ·
Is your data ready for a ransomware attack? 15 questions to answer before it happens
Most teams learn about ransomware from the ransom note. Fifteen questions on detection, protected copies, recovery, people and infrastructure show where your team stands, and what IBM FlashSystem changes at the storage level.
Most teams find out about ransomware from the ransom note. By then the encryption has run for hours, the copies may be encrypted too, and the real question is no longer how to stop the attack but how fast you can come back.
That question has an answer only if it was asked before the attack. We put together 15 questions that every IT team should be able to answer today. “I don’t know” is an answer too: it shows where to start.
Five areas to check
Detection. Do you have automatic detection of encryption, and do you know who gets the first alert? How long does it take from the start of an attack to that alert? And do you watch for unusual activity in the storage itself, not only on servers and the network?
Protected copies. Do you have copies nobody can change or delete, not even an administrator with a stolen account? How often are they taken, how far back do they go, and are they separated from the main environment in network, accounts and permissions alike?
Recovery. How would you find the last clean copy from before the attack? How long would it take to bring back your critical systems? Have you run a full recovery test in the last 12 months, and is it decided which systems come back first and who makes that call?
People and process. Does the team know where the written response plan is, who must learn about the attack first and how to reach them out of hours? Is there a ready procedure for informing management, customers and regulators, for example under NIS2?
Infrastructure. How much of your data sits on storage without built-in ransomware protection? And what does one day of downtime of your core systems cost?
The full list, ready to go through with your team, is a free PDF: get the checklist. It takes about ten minutes.
What changes when the storage watches too
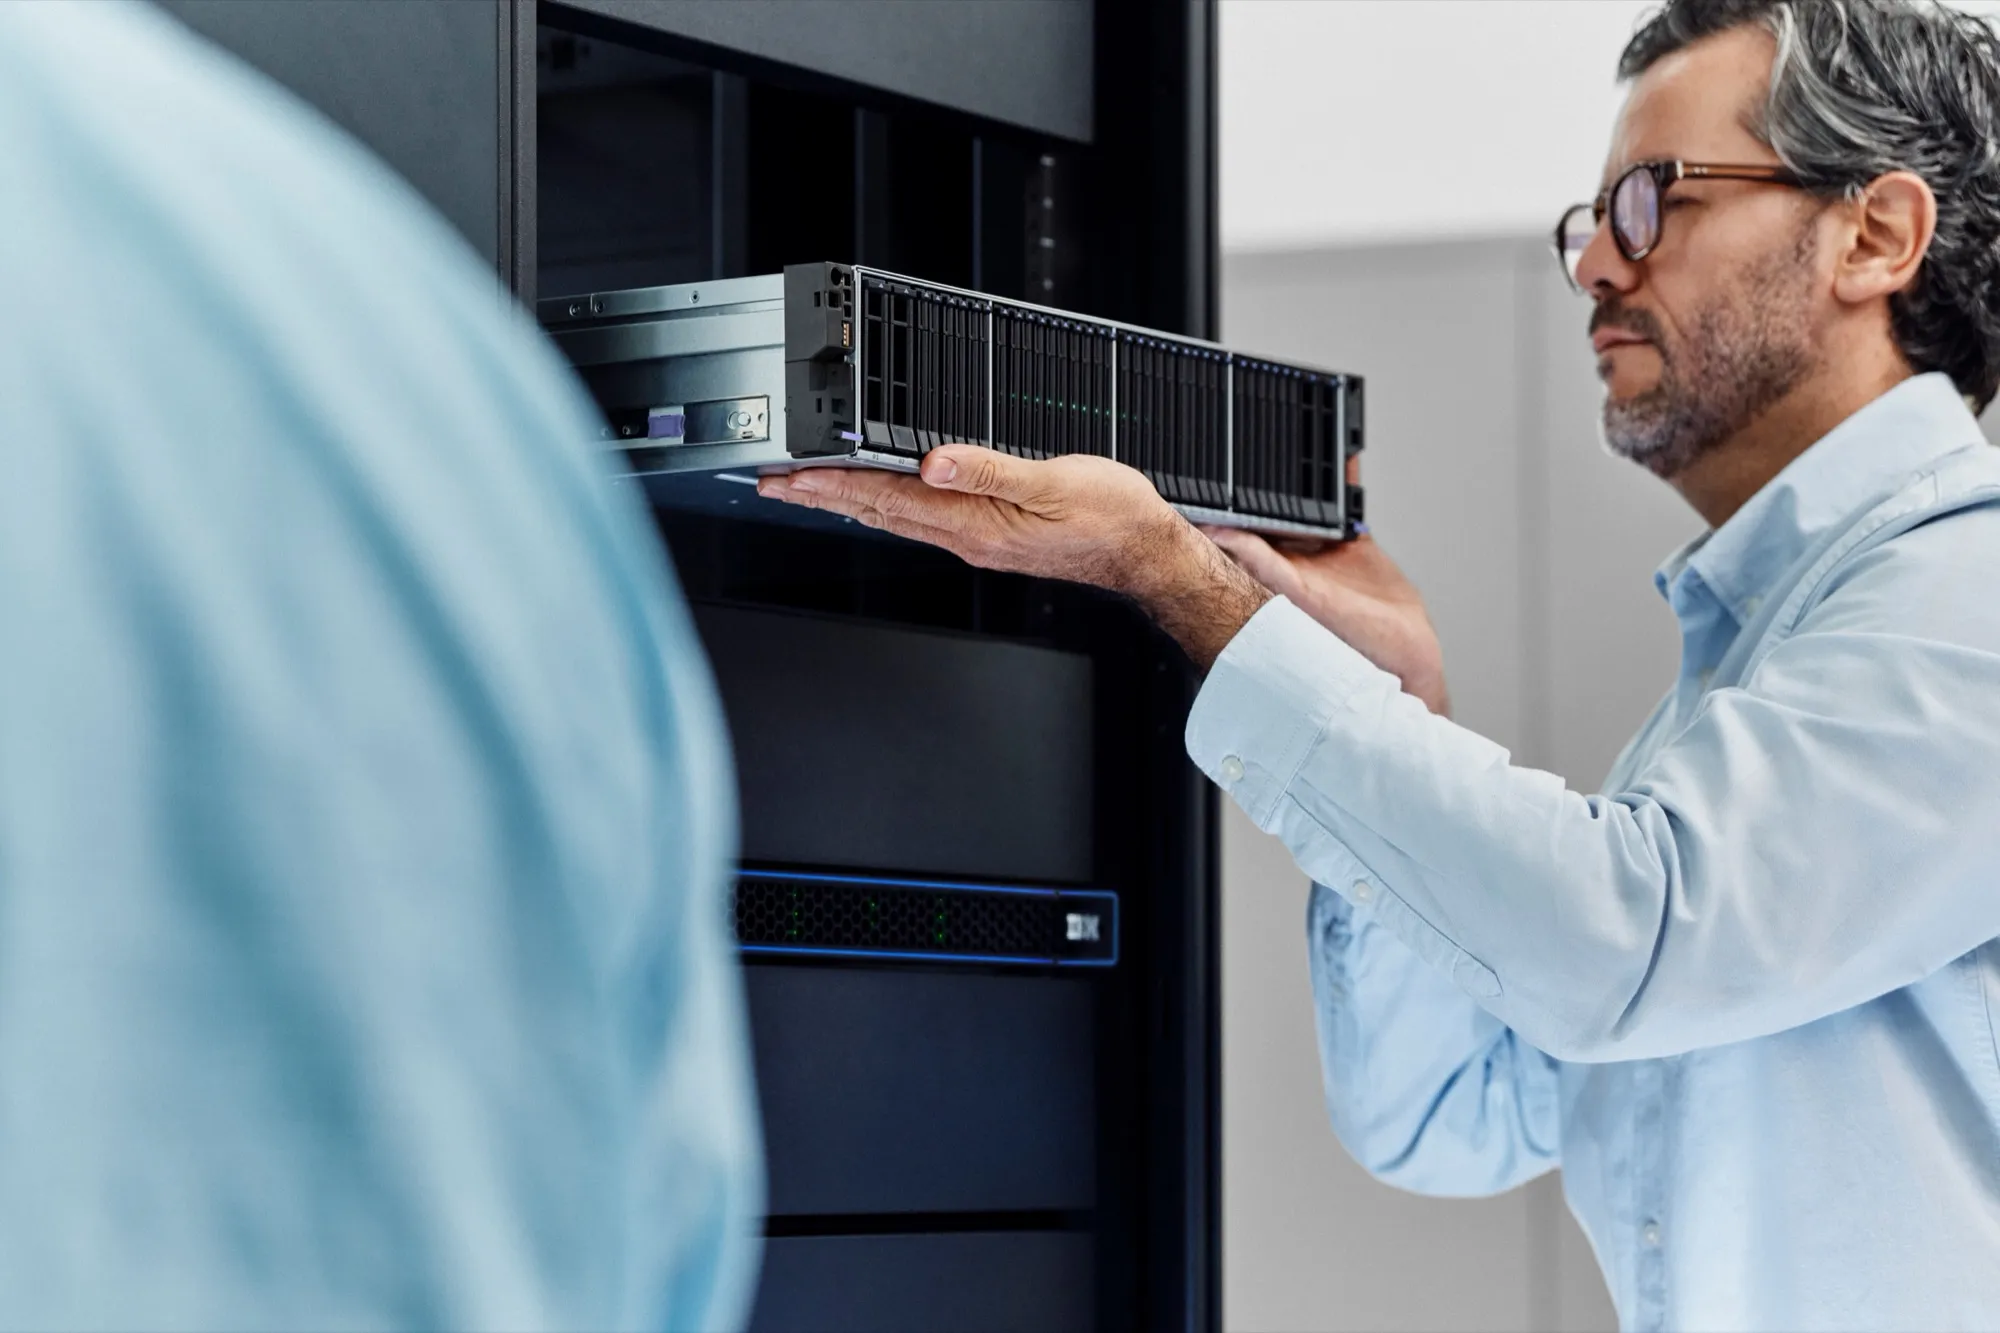
Detection on servers and the network sees what the attacker lets it see. The storage sees every write. The new generation of IBM FlashSystem uses that:
- Detection inside the drive. The fifth-generation FlashCore Module analyses every I/O and, according to IBM, detects ransomware in under 60 seconds. The analysis runs in the module, so the controllers stay free for your applications.
- Copies that cannot change. Safeguarded Copy keeps copies that cannot be altered or deleted, and IBM states that a clean copy can be restored in about 60 seconds.
- No downtime. Policy Based High Availability provides 100% data availability over three years, under IBM’s terms.
The figures are IBM’s own, from its client presentation of February 2026, and apply under IBM’s conditions. The three models, 5600, 7600 and 9600, are described in our earlier news.
Where we help
If some of the 15 questions have no confident answer, we can go through them with your team: we review your storage and copies, show where the risks are in an attack, and propose the model and capacity for your workload. We implement it, move the data to a plan agreed with you, and our storage team in Sofia stays with you after go-live.